

How to Create a Risk Register for Pre-Sale Planning
How to create a risk register for pre-sale planning starts with a simple idea: buyers pay more for businesses they understand, trust, and believe can operate without ugly surprises. In mergers and acquisitions, a risk register is a living document that identifies, ranks, assigns, and tracks the issues that could reduce valuation, delay diligence, or derail a transaction. For founders, it is not corporate bureaucracy. It is a practical pre-exit planning tool that turns uncertainty into action. I have seen owners lose leverage because they treated risks as scattered conversations instead of documented, managed items. A well-built risk register changes that dynamic.
Pre-sale planning means preparing a business for a future transaction before a letter of intent appears. It includes legal cleanup, financial normalization, operational documentation, customer concentration analysis, leadership readiness, cybersecurity review, tax planning, and seller mindset. A risk register sits at the center of that work because it gives every issue a name, an owner, a due date, and a mitigation plan. It also helps founders communicate clearly with advisors, from M&A attorneys to accountants to quality of earnings providers. If you are building a pre-exit planning toolkit, this document belongs near the top.
Why does this matter so much? Because most deals do not get hurt by one dramatic disaster. They get weakened by many small unresolved problems: unsigned contractor IP assignments, stale customer agreements, sales tax exposure, inconsistent margin reporting, founder-dependent relationships, or a top employee with no retention plan. Buyers do not just price current performance. They price future risk. The more risk they perceive, the lower the multiple, the more holdbacks they request, and the more aggressive they become in diligence. A risk register gives founders a disciplined way to reduce that perceived risk before buyers ever enter the data room.
This article is the hub for pre-exit planning tools, so it covers the full framework rather than one narrow tactic. Below, you will learn what a pre-sale risk register should include, how to score risks, who should own them, how often to update the register, and how to use it alongside other preparation tools such as diligence checklists, SOP libraries, financial dashboards, and organizational charts. Done right, this one document becomes the operating system for exit readiness.
What a risk register is and why it belongs in every pre-exit planning toolkit
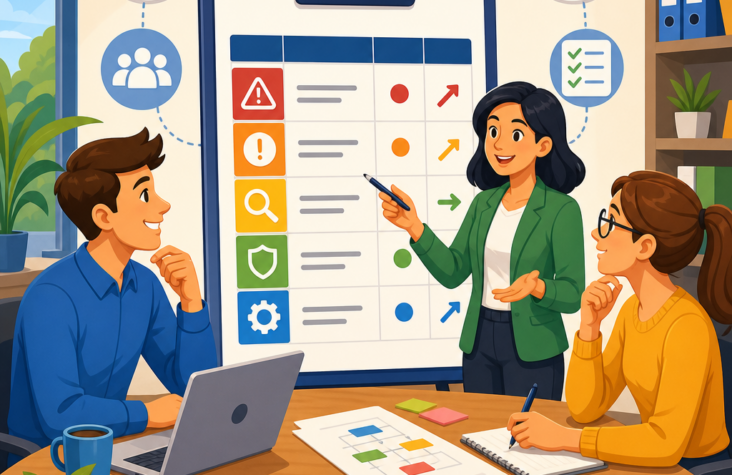
A risk register is a structured list of risks that could affect a business outcome. In pre-sale planning, the outcome is a successful transaction on favorable terms. The register usually includes the risk description, category, likelihood, impact, overall rating, mitigation plan, owner, target resolution date, status, and notes. Large companies use risk registers for enterprise governance, but smaller founder-led businesses can use the same concept in a simpler, more useful form.
The reason it belongs in every pre-exit planning toolkit is straightforward: it creates visibility. Most owners already know where some problems exist, but that knowledge often lives in fragments. The CFO knows the revenue recognition issue. The controller knows accounts receivable aging is messy. The COO knows one plant manager has undocumented tribal knowledge. The founder knows two clients represent 34 percent of revenue. The outside attorney knows an old lawsuit is still technically open. A risk register pulls those facts into one place so the company can act before a buyer weaponizes them.
It also improves decision quality. Not every issue deserves the same energy. A missing signature on a minor vendor agreement is not equivalent to payroll tax exposure or a cybersecurity weakness in a healthcare SaaS platform. The register forces prioritization. It helps management focus on the risks that will materially affect valuation, representations and warranties, working capital adjustments, earn-out structure, or deal certainty.
As the hub page for pre-exit planning tools, think of the risk register as the command center that connects the rest of the toolkit. Your financial cleanup checklist feeds it. Your legal diligence checklist feeds it. Your HR succession plan feeds it. Your SOP and documentation library reduces items on it. Your data room eventually proves that many of its items were resolved. That is why this tool is foundational rather than optional.
What risks to include before a sale
The most effective risk registers are organized by category. That makes it easier to scan patterns and assign the right people. In pre-sale planning, the major categories usually include financial, legal, tax, operational, commercial, technology, cybersecurity, HR, regulatory, and transaction-specific risks.
Financial risks include inconsistent monthly closes, margin volatility, poor accounts receivable aging, inventory inaccuracies, weak forecasting, unexplained add-backs, customer credits not properly accrued, and revenue recognition problems. If a quality of earnings report would likely challenge your numbers, that belongs in the register.
Legal risks cover unsigned contracts, missing board approvals, outdated corporate records, IP ownership gaps, litigation exposure, employment disputes, contractor classification problems, and lease clauses that trigger on a change of control. Many founders underestimate how often basic legal housekeeping causes friction in diligence.
Tax risks are frequent deal disruptors. Common examples include unpaid sales tax in nexus states, payroll tax issues, aggressive deductions with poor support, transfer pricing concerns, and entity structure problems that create inefficient after-tax proceeds. If a buyer’s tax advisors will flag it, the seller should already have it documented.
Operational risks include undocumented processes, founder dependence, poor reporting cadence, weak inventory controls, supplier concentration, lack of backup leadership, and systems that only one employee knows how to run. Buyers want repeatability. Anything that threatens continuity should be listed.
Commercial risks include customer concentration, declining retention, channel dependence, pricing compression, lack of contract renewals, key account vulnerability, and pipeline weakness. A business with 40 percent of revenue tied to one channel partner has a commercial risk whether management likes that fact or not.
Technology and cybersecurity risks matter in nearly every sector now, not just software. Outdated software licenses, unsupported systems, weak access controls, no incident response plan, poor backup practices, or undocumented code ownership can hurt trust fast.
HR risks include retention concerns, weak management depth, compensation misalignment, lack of employment agreements, no incentive plan for key employees, and culture fragility. Founders often assume buyers only buy numbers. Sophisticated buyers always assess whether the team can carry the business after closing.
How to structure the register so it is usable
The best risk register is the one your team will actually maintain. That means it should be simple enough to use weekly but detailed enough to support a serious sale process. A spreadsheet works for many lower middle-market businesses. Larger companies may use project management or governance software, but the structure is what matters most.
| Field | Purpose | Example |
|---|---|---|
| Risk ID | Unique reference for tracking | L-03 |
| Category | Groups related issues | Legal |
| Risk Description | States the issue clearly | Three contractor IP assignments missing |
| Likelihood | Chance of becoming a deal issue | High |
| Impact | Potential damage to value or closing | High |
| Risk Score | Combines likelihood and impact | 9/9 |
| Mitigation Plan | Defines the response | Obtain signed assignments within 30 days |
| Owner | Single accountable person | General Counsel |
| Target Date | Deadline for resolution | June 30 |
| Status | Progress signal | In progress |
A few rules matter here. First, each risk needs one owner, not three. Shared accountability usually means no accountability. Second, the description should be factual, not vague. “Compliance issue” is weak. “Sales tax registration incomplete in two states with ecommerce nexus” is usable. Third, the mitigation plan should be action oriented. “Monitor situation” is not a plan. “Engage tax advisor, quantify exposure, register, and negotiate payment plan if needed” is a plan.
How to score and prioritize risks
A practical risk register needs a scoring method. The easiest model uses likelihood and impact, each rated low, medium, or high, or numerically from one to three. Multiply them to produce an overall score. A high-likelihood, high-impact issue becomes top priority. A low-likelihood, low-impact issue may stay on the list but receive less urgency.
For pre-sale planning, impact should be judged against transaction consequences, not just operational irritation. Ask whether the issue could reduce EBITDA quality, shrink valuation multiple, create indemnity exposure, delay closing, trigger a working capital dispute, or cause the buyer to demand more rollover equity or a longer earn-out. That is the lens that matters.
For example, if a manufacturer has one environmental compliance question at a small facility, that may be low likelihood but high impact. If a services firm has no signed invention assignment agreements from early developers of a proprietary internal platform, that may be medium likelihood but very high impact because ownership questions spook buyers. If a company has customer concentration above 25 percent with no long-term contract, that is typically both high likelihood and high impact.
Some sellers also add a third factor: detectability. In other words, how likely is a buyer to discover this during diligence? In M&A, that factor is often less helpful than founders think because sophisticated buyers discover more than expected. A better assumption is this: if it matters, it will probably be found. Build the register around that reality.
Who should build and maintain it
One reason risk registers fail is that founders treat them like a side project for the finance team. That is too narrow. Pre-sale risk lives across the business, so the register should be cross-functional. The founder or CEO sets the tone. The CFO or controller often manages the process. Legal, HR, operations, sales, and technology leaders contribute their respective items. If the company has an outside M&A advisor, that advisor can help frame risks through a buyer’s lens.
In smaller businesses, the team may be founder, accountant, attorney, and operations lead. In larger companies, it may become a monthly exit readiness committee. Either way, the process needs cadence. A register that gets created once and then ignored is useless. I prefer monthly reviews when a company is 12 to 24 months from a potential process, and biweekly reviews once active sale prep begins.
The CEO’s role is especially important. If leadership punishes people for surfacing problems, the register becomes fiction. The culture has to reward honesty. Good pre-sale planning is not pretending risks do not exist. It is proving the company knows where they are and is managing them responsibly.
How to use the register with other pre-exit planning tools
This page is the hub for pre-exit planning tools, so the biggest mistake would be treating the risk register like a standalone artifact. It becomes powerful when connected to the rest of the toolkit.
Your diligence checklist identifies the categories to review. Your risk register records what those reviews uncover. Your data room stores the documents that prove resolution. Your financial dashboard measures whether margin, churn, concentration, and working capital trends are improving. Your SOP library reduces operational and founder-dependence risk. Your org chart and retention plan reduce HR and transition risk. Your tax review and legal audit clear out hidden liabilities. All of those tools feed the register and, ideally, shrink it over time.
For example, a founder preparing to sell an agency might uncover these items: no documented onboarding process, two clients representing 31 percent of revenue, inconsistent timesheet coding affecting gross margin visibility, and no employment agreements for senior account leaders. Those risks would sit in the register, while mitigation work would happen inside other tools: SOP documentation, customer diversification plan, finance process update, and HR contract project.
Used this way, the register becomes the board that tracks exit readiness progress. It tells you not just what is wrong, but whether the business is becoming more transferable, more defensible, and more valuable.
Common mistakes founders make with pre-sale risk registers
The first mistake is starting too late. If you begin six weeks before a buyer enters diligence, the register becomes a panic list instead of a planning tool. The second is being too vague. Generic statements hide urgency. The third is confusing problems with excuses. Buyers do not care why an issue exists nearly as much as they care whether you can quantify it and fix it.
A fourth mistake is overengineering the document. Founders do not need enterprise risk software to prepare for a sale. A disciplined spreadsheet reviewed consistently will outperform a fancy platform nobody updates. A fifth is ignoring “soft” risks like founder dependence, leadership fragility, and customer relationship concentration because they feel harder to quantify. Those issues often drive structure more than hard financials do.
The last mistake is failing to close the loop. A risk should not just move from red to green because someone says it is handled. The company should attach proof: signed contracts, updated policies, tax filings, documentation, or resolved financial schedules. That proof later belongs in the data room.
How to start building your risk register this week
Start with a working session. Gather the founder, finance lead, legal counsel, operations leader, and anyone else who sees risk clearly. Ask one question: what would a serious buyer worry about in this business? Capture everything without debating solutions first. Then categorize, score, assign owners, and create due dates. Keep the first version simple. You can refine it as patterns emerge.
Next, sort by score and attack the top five items first. That is how momentum starts. If the biggest risks are customer concentration, weak monthly closes, unsigned IP assignments, poor contract organization, and founder-led sales, your next quarter should reflect that. Build mitigation projects around them.
Finally, review monthly and update honestly. A risk register is valuable because it tells the truth early, when the company still has time to respond. That is the essence of pre-sale planning.
A risk register will not sell your business by itself. But it will make your business easier to understand, easier to diligence, and easier to trust. That is exactly what buyers pay for. If you are serious about pre-exit planning tools, make this your hub document and let every other checklist, audit, and cleanup effort feed into it. Start now, keep it current, and turn risk from a valuation discount into a strategic advantage.
Frequently Asked Questions
What is a risk register in pre-sale planning, and why does it matter before selling a business?
A risk register in pre-sale planning is a structured document that captures the issues that could negatively affect valuation, slow down due diligence, weaken buyer confidence, or even cause a deal to fall apart. In practical terms, it is a list of known risks, along with an assessment of how serious each risk is, who owns it internally, what evidence supports it, what actions are being taken, and what the current status looks like. In the context of mergers and acquisitions, this is not just an internal management exercise. It becomes a decision-making tool that helps founders and leadership teams address weaknesses before a buyer discovers them first.
It matters because buyers reward clarity and penalize uncertainty. If a company can explain its risks clearly, show how they have been assessed, and demonstrate that there is a plan in place to reduce or manage them, the business appears more mature, credible, and easier to underwrite. By contrast, unmanaged risks often lead to price chips, indemnity demands, delayed timelines, expanded diligence requests, or heightened escrow requirements. A well-built risk register helps the seller take control of the narrative by identifying issues early and turning vague concerns into concrete remediation steps. That makes the business easier to understand and easier to trust, which is exactly what supports a smoother process and a stronger outcome.
What types of risks should be included in a pre-sale risk register?
A strong pre-sale risk register should include any issue that could influence enterprise value, buyer appetite, transaction timing, or post-close integration confidence. That usually means looking well beyond financial risks alone. Common categories include financial reporting issues, customer concentration, supplier dependency, legal disputes, compliance gaps, tax exposure, cybersecurity weaknesses, intellectual property ownership problems, employee retention concerns, key-person dependence, contract assignability issues, operational bottlenecks, quality control issues, and market or regulatory changes that could materially affect future performance. If a risk could cause a buyer to question sustainability, transferability, or predictability, it belongs in the register.
Founders should also include softer but still material risks, such as undocumented processes, inconsistent KPI reporting, overreliance on informal relationships, lack of second-line management, or weak data room readiness. These may not look dramatic on their own, but in diligence they often signal execution risk and increase buyer caution. The most effective risk registers are not generic templates filled with abstract categories. They are specific to the business, the industry, and the expected buyer lens. A strategic acquirer may focus on integration, contracts, and customer overlap, while a financial buyer may care more about recurring revenue quality, margin durability, and management depth. The goal is to think like a buyer and document the risks that would matter most to someone evaluating whether your company is worth paying a premium for.
How do you build a risk register for pre-sale planning step by step?
Start by gathering the right internal perspectives. Pre-sale risks rarely sit in one department, so the process should involve leadership across finance, legal, operations, sales, HR, IT, and compliance. Begin with a structured risk identification session and ask a simple question: what could reduce value, create diligence friction, delay closing, or make a buyer nervous? From there, list each risk in plain language. Avoid vague entries like “operational issues” and instead write specific statements such as “40% of revenue tied to one customer with annual renewal in six months” or “three core software modules lack documented IP assignment from original contractors.” Specificity is what makes the register useful.
Next, score each risk based on likelihood and impact. Many companies use a simple high-medium-low system, while others assign numeric ratings for probability, financial effect, timing sensitivity, and buyer perception. Then assign an owner to every item. A risk without clear accountability usually remains unresolved. After ownership is assigned, document current controls, remediation actions, deadlines, status updates, and supporting evidence. For example, if customer concentration is a major risk, the mitigation plan might include extending key contracts, accelerating pipeline diversification, and preparing a retention strategy. If accounting controls are weak, remediation may involve a quality of earnings review, revised close procedures, or outside advisory support. The register should also distinguish between inherent risk and residual risk, meaning the level of exposure before and after planned mitigation. Finally, review and update it regularly. A risk register is a living document, not a one-time exercise. As the company improves readiness, some risks shrink, new ones emerge, and priorities change based on deal timing and buyer expectations.
How detailed should a pre-sale risk register be, and what information should each entry contain?
A pre-sale risk register should be detailed enough to support action, accountability, and buyer readiness, but not so bloated that it becomes impossible to maintain. The right level of detail allows leadership to understand the issue quickly, evaluate its seriousness, and decide what to do next. Each entry should typically include a clear risk description, risk category, likelihood, potential impact, business area affected, transaction relevance, assigned owner, mitigation plan, target completion date, current status, and any evidence or notes that support the assessment. Many companies also include a field for buyer sensitivity, which helps distinguish ordinary operating risks from issues likely to trigger intense diligence scrutiny or valuation pressure.
Good entries are specific, measurable, and decision-oriented. For example, instead of writing “compliance risk,” a better entry would explain which regulation is involved, what the gap is, what the possible financial or legal consequence could be, and what corrective action is underway. If a risk is related to contracts, the entry should note how many contracts are affected, whether change-of-control clauses exist, and whether consents may be required before close. If the issue is management concentration, identify which individuals are critical, what processes are undocumented, and whether succession or retention planning is in place. This level of detail makes the register far more useful for both internal execution and external deal preparation. It also helps management separate noise from material issues, so attention stays on the risks that truly influence transaction outcomes.
When should founders create a risk register, and how can it improve valuation and deal certainty?
Founders should create a risk register well before launching a sale process, ideally 12 to 24 months ahead if time allows. That timeline gives the company room to identify weaknesses, prioritize fixes, gather documentation, and show measurable progress before buyers begin formal diligence. Starting early is important because many meaningful risks cannot be solved overnight. Customer concentration, management depth, financial reporting quality, recurring contract terms, and legal clean-up often require months of sustained work. If the register is only created after an advisor is hired or after buyer questions begin arriving, the company is usually reacting under pressure rather than controlling the process from a position of strength.
Used properly, a risk register can improve both valuation and deal certainty. On valuation, it helps preserve EBITDA quality, reduce perceived earnings risk, and support the story that future cash flows are dependable. On deal certainty, it reduces surprises, shortens back-and-forth during diligence, and gives buyers confidence that management is prepared, transparent, and credible. That confidence matters. Buyers do not expect a business to be risk-free. They expect the seller to understand the risks, quantify them where possible, and show how they are being managed. A disciplined risk register helps founders do exactly that. It creates a roadmap for remediation, strengthens internal readiness, and makes the business more understandable to an outside party evaluating whether it is worth paying top value for. In that sense, the register is not just a defensive tool. It is part of the broader strategy for presenting a cleaner, stronger, and more investable company at the moment when scrutiny is highest.